
Open source has always been foundational to cloud-native computing. Kubernetes itself is the product of thousands of contributors, but the platforms we build around it depend on an even broader ecosystem of projects spanning networking, storage, identity, backup and recovery, cluster lifecycle management, and more.
At Broadcom, contributing to that ecosystem has long meant more than consuming open source software. Our engineers contribute code, participate in communities, work alongside maintainers, and help projects evolve based on what we learn from running cloud-native technologies at enterprise scale.
Increasingly, we’re also thinking about another dimension of that responsibility: security.
The cloud-native world is expanding, and AI is shifting how we build and secure software. That opens up fresh ways to catch security risks while doubling down on what always works, which is direct, open collaboration with upstream communities.
Security Is a Shared Responsibility
Cloud-native infrastructure is inherently interconnected and a Kubernetes environment isn’t simply Kubernetes. It depends on projects responsible for cluster lifecycle, identity, storage, networking, backup and recovery, and many other capabilities. A security improvement in one of those projects can benefit far more than a single product or vendor.
That’s one reason we’ve expanded some of our upstream work to include proactive security research across open source projects that are important to the cloud-native ecosystem.
Our engineers work across projects including etcd, Cluster API, Pinniped, and Velero, where they work to identify potential issues, investigate them with project maintainers, and help move validated findings toward resolution.
The objective isn’t simply to find more vulnerabilities. It’s to help make the software that all of us depend on safer and more resilient.
Finding an Issue Is Only the Beginning
One thing this work has reinforced is that identifying a potential security issue and resolving one are very different things.
Modern AI tools can help engineers analyze large codebases and surface potential problems at a scale that would have been extraordinarily difficult through manual analysis alone. That’s a powerful capability, and one we believe can augment the work security researchers and software engineers are already doing.
But an AI-generated finding isn’t automatically a vulnerability.
Someone still has to understand the code. Is the behavior actually exploitable? Under what conditions? Which versions are affected? Is the proposed remediation appropriate? Could a fix introduce a regression somewhere else?
And in open source, there’s another critical participant in that process: the maintainer.
Maintainers understand the architecture, history, and operational realities of their projects. Responsible security work therefore requires collaboration by bringing potential findings to the appropriate project, validating them together, developing and reviewing fixes, and coordinating disclosure and releases when necessary.
AI can accelerate parts of that process. It doesn’t replace it.
From Findings to Upstream Fixes
We have seen the tangible impact of that upstream collaboration across several core projects:
- Velero: The work contributed directly to fixes for two published GitHub Security Advisories in the 1.18.3 release.
- etcd: Research not only resolved issues across supported release branches but also updated the project’s threat model.
- Cluster API and Pinniped: Findings were validated with community maintainers to deliver upstream remediations.
Project Highlights
- Velero (v1.18.3): Coordinated and resolved security advisories GHSA-vrfp-2×59-hcfm and GHSA-8gv3-c356-fw76 upstream in release v1.18.3 (integrated downstream in VMware vSphere Kubernetes Service (VKS) Add-ons v3.7.0+20260924), authoring patch remediation and performing end-to-end backup/restore validation.
- etcd (v3.5.33 / v3.6.14 / v3.7.1): Discovered and disclosed CVE-2026-73500, contributed upstream patch remediation backported across releases v3.5.33, v3.6.14, and v3.7.1 (integrated downstream in vSphere Kubernetes Release (VKr) Oct Releases), and updated distributed state storage threat models.
- Cluster API (v1.12.11, v1.13.5, v1.14.0): Screened and validated findings upstream, contributing bug fixes and hardening controller reconciliation logic.
- Pinniped (v0.47.0): Identified authentication credential handling vulnerabilities under CVE-2026-59269, developed upstream remediation released in v0.47.0 (integrated downstream in VKr Oct Releases), and verified identity provider integration tests.
Impact by the Numbers
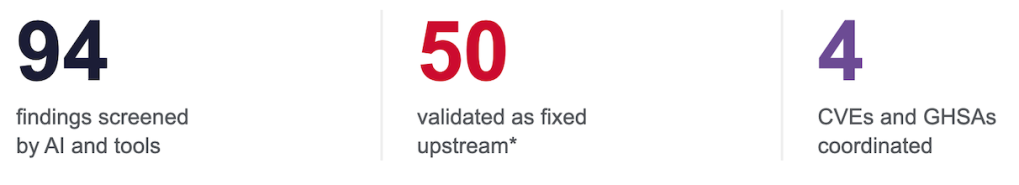
*Validated as Fixed Upstream: Pull Request with a fix was merged upstream and cherry picked when appropriate.
From AI Findings to Upstream Security Improvements
Identifying potential vulnerabilities is only the beginning. Turning AI-generated findings into meaningful security improvements requires careful validation, collaboration with upstream maintainers, and an understanding of each project’s architecture and threat model.
As Pushkar Joglekar, a Kubernetes maintainer who led this vulnerability discovery research, explained, an important part of the process was ensuring that findings were reviewed from a maintainer’s perspective before being shared with upstream projects.
“One non-negotiable requirement was to have every AI-generated finding filtered through a maintainer persona, so that when we request maintainer review time – a highly constrained resource – we are not wasting it by disclosing raw findings, which are often overstated or reflect intentional design decisions.”
This approach helped ensure that maintainer attention was focused on findings that warranted further investigation rather than potential issues already understood or accounted for in the project’s design.
For etcd, this collaboration also created opportunities to strengthen how security issues are evaluated. Benjamin Wang, an etcd maintainer, described how the work extended beyond validating vulnerabilities and developing patches to refining the project’s threat model and clarifying vulnerability boundaries.
These outcomes were not limited to identifying security vulnerabilities. In the Cluster API project, the research also provided opportunities to evaluate existing security practices and identify areas for additional hardening.
As longtime Cluster API maintainers Fabrizio Pandini and Stefan Büringer observed:
“Usage of AI models provides a new valuable source of input for this work, which led to a series of useful robustness / hardening improvements.”
They also emphasized that the absence of major findings reinforced the value of the project’s established security processes and ongoing collaboration with the Kubernetes Security Response Committee.
Together, these experiences demonstrate that AI-assisted vulnerability discovery is most valuable when paired with maintainer expertise and established upstream security practices. The result is not simply more findings, but better-informed security decisions and opportunities to strengthen the resilience of the projects the cloud-native ecosystem depends on.
Strengthening the Ecosystem We All Depend On
There is a tendency in technology to talk about open source contribution primarily in terms of features: a new capability contributed upstream, a new project donated to a foundation, or a new integration built with another project.
Those contributions matter.
But maintaining a healthy open source ecosystem also means doing some of the less visible work required to make that ecosystem dependable. This includes testing, reviewing, fixing, documenting, maintaining, and increasingly, proactively looking for ways to improve security.
For Broadcom, that’s an important part of what upstream participation means.
We build products using cloud-native open source technologies. Our customers rely on those technologies. Our engineers participate in the communities that maintain them.
When we combine our engineering expertise with emerging tools like AI to identify an issue, collaborate with maintainers, and contribute an improvement upstream, the benefit extends well beyond Broadcom.
It strengthens the shared foundation we’re all building on.
And as cloud-native infrastructure becomes the foundation for the next generation of applications and AI workloads, continuing to invest in that foundation may be one of the most important contributions we can make.
Resources
- Learn more about VKS
- Running agent substrate on VKS
- Advancing the Cloud-Native Ecosystem Through Open Collaboration
Discover more from VMware Cloud Foundation (VCF) Blog
Subscribe to get the latest posts sent to your email.